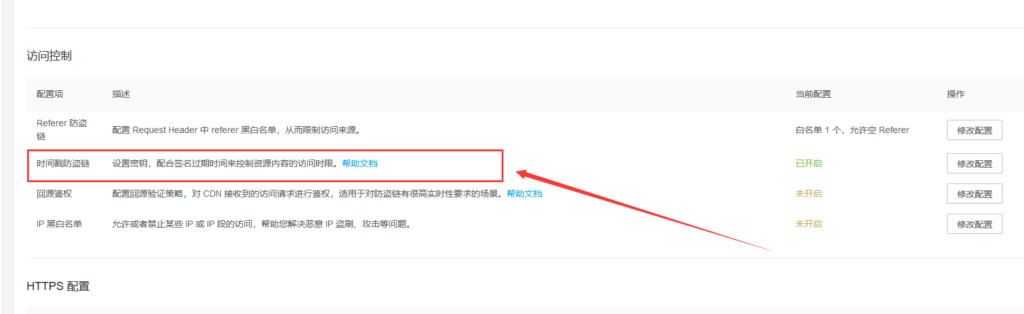
The CDN supports various防盗链 configuration options; different防盗链 methods are suitable for different application scenarios. It is recommended to configure them accordingly. fusecdn => domain name supervising => configure => access control Set up
1: Referer防盗链机制: Only HTTP requests that include the appropriate Referer HTTP header can access resources; however, from a technical perspective, the Referer header can be forged, which poses certain security risks.
2: Timestamp-based防盗链机制 – the URL is accessed using the `e` and `token` parameters; `e` represents the expiration time. However, as long as the URL is captured, the resource can be accessed; this method is suitable for scenarios where the resource should only be accessed a limited number of times.
3: Origin Authentication – You can try this approach: every time a request is made to a CDN image, the request will include custom authentication parameters sent to your own server for verification. Only if the server successfully authenticates the request and returns an HTTP status code of 200 will the image resource be made available to the user; otherwise, the image will not be served.
4: IP allowlist/denylist – This feature is suitable for managing IP access within a specific network segment but is not recommended for use on official websites; only users listed in the IP allowlist can access your images.
https://developer.qiniu.com/fusion/4960/access-control-configuration
☆ It is recommended to use the third type of source authentication and the fourth type of IP allowlist/denylist for access control.